 Sarah Miller
On November 16, 2026, visitors to some of the world's most visited websites were served malware from a script those sites already trusted. Scott Helme of Report URI reported that an attacker injected malicious JavaScript into customer projects on Optimizely's Web Experimentation platform, and that the code was then delivered from Optimizely's own content delivery network. The firm's crawl found the code in 188 snippets belonging to 178 organizations, including Zoom, the BBC, CNN, Salesforce, GitLab, IKEA, HSBC and Equifax. Helme said the real number is likely higher, because the team could only check the snippets it found in time.
Optimizely confirmed the incident at 01:02 UTC on November 17, which was 8:02 p.m. Eastern on November 16. An unauthorized party, the company said, "exploited a vulnerability in Experimentation and used it to add malicious JavaScript to some customer projects." It said it had fixed the vulnerability, removed the injected code, taken steps to secure affected user accounts and added protections to prevent unauthorized code from being delivered. To BleepingComputer, Optimizely was more specific: the weakness was in the Experimentation account signup flow. The company said it blocked access to that path, ended active sessions, revoked tokens, reset access for affected accounts, blocked the code from being delivered at Cloudflare and notified all affected customers. It has not published a customer count.
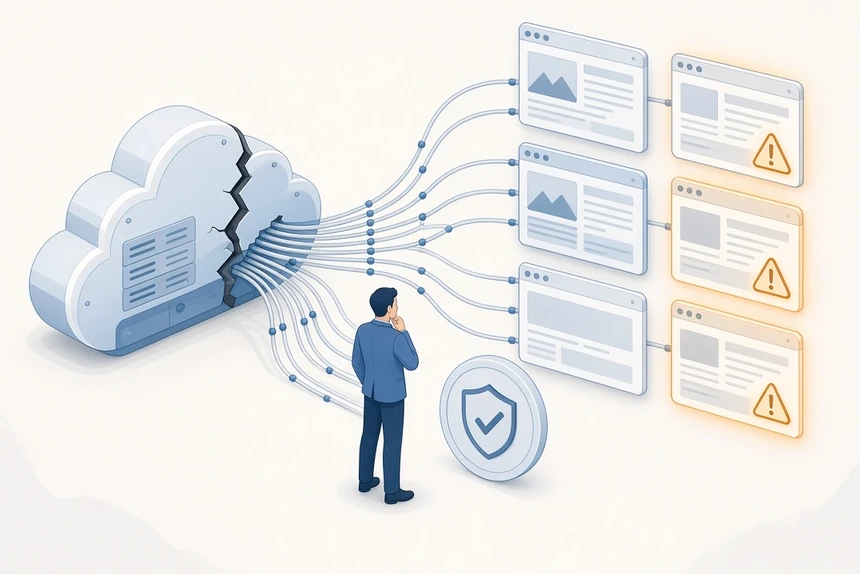
This was not a case in which each of those websites had to be hacked on its own. The attackers reached Project JavaScript, an optional field of custom code that runs on every page that loads an Optimizely snippet. Report URI found that the rest of each snippet was left untouched, and that the file was still served from cdn.optimizely.com with Optimizely's certificate. Some customers host the snippet on their own domain; those copies were affected too, the firm said, because the content still comes from the same project.
The lesson for enterprise architects is not only that a vendor had a bad day. It is that a centralized third-party service, once trusted in production, becomes a distribution channel. One compromised control plane can reach hundreds of otherwise unrelated sites.
What The Payload Did
According to Report URI's analysis, which BleepingComputer independently corroborated on several affected sites, the injected loader pulled a payload from an attacker-controlled domain, or, in some versions, carried a full copy of the code that could run if that domain was blocked. The payload swapped cryptocurrency wallet addresses for the attacker's, skimmed payment card details submitted in a site's own form fields, and collected cookies and screenshots. A card skimmer was added at 13:43 UTC. Card numbers entered in a cross-origin payment iframe, such as Stripe or Adyen hosted fields, were outside its reach.
The same payload also attempted to deliver the Coruna and DarkSword iOS exploit kits to iPhone and iPad visitors. SecurityWeek reports that Hudson Rock confirmed a connection to that exploit-kit infrastructure, but said the evidence does not establish a successful device compromise. The Hacker News reports that Cynet, which retrieved a second stage with an emulated iPhone browser, described what it saw as conditional delivery, not a successful compromise of a physical device. We have no independent confirmation of how many visitors, if any, were successfully exploited that way.
Report URI recorded roughly $7,000 in cryptocurrency reaching wallets embedded in the payload by the evening of November 16. Some of those wallets had been used before this incident, so that figure should not be read as a precise loss total for this campaign. The firm later said the wallets were emptied early on November 17. It has no visibility into how many cards, cookies or screenshots were taken.
The first Optimizely injection in Report URI's timeline is dated 04:21 UTC on November 16, in the BBC's snippet. A mass cleanup began around 20:40 UTC. By 21:52 UTC only one of the 188 infected snippets still carried the code, and by 23:11 UTC the firm observed that all of the infected files it was watching had been cleaned. As of the morning of November 17, Optimizely's status page still listed the incident as monitoring and unresolved.
Salesforce told BleepingComputer that, as a precaution, it was confirming Optimizely scripts were disabled across preview and production instances, and that it would notify affected customers if it identified unauthorized access to their data. That is a containment step, not evidence that Salesforce's own systems were breached.
What Remains Open
Optimizely has not, in the public notices we read, explained how a weakness in the signup flow became write access to so many unrelated customer projects, how long the vulnerability had been present, or whether any attacker access remains. Report URI noted that Smartsheet's snippet was cleaned and then re-infected with a hidden, base64-encoded version of the loader, which indicated the attacker still had access at that point. The company has not published a complete list of affected projects. The 178-organization figure is a researcher's observed set, not an official census.
Researchers have also described an earlier wave of a similar injector through scripts from other vendors, including Kissmetrics, StorifyMe and Minute Media, beginning before the Optimizely injections. Those findings are not a claim that the same Experimentation vulnerability was used elsewhere, and we do not treat them as part of Optimizely's confirmed incident. This is also Optimizely's second disclosed security issue in 2026. In February, the company confirmed that a voice-phishing attack had reached some internal systems. Nothing published so far links the two events.
Why This Is An Architecture Problem
Helme's conclusion is the one that should sit with enterprise architects: "A website can be compromised through a third-party dependency without its own code or infrastructure ever being breached."
The blast radius here came from concentration. Hundreds of sites loaded a script from a shared vendor service and treated that host as trusted. When the custom-code field in those projects was changed, every page that loaded the snippet became a delivery path. A Content Security Policy that simply allowed cdn.optimizely.com could not stop the payload, because the malicious code arrived from that same trusted host. Report URI crawled 256 of the affected organizations' own hosts and found that 68 had no CSP at all, 50 had a policy that still allowed both the payload and the data theft, and only 24 blocked the payload. The firm also noted that Optimizely's documentation tells customers to allow 'unsafe-eval', and that an inline copy of the payload still ran at HSBC even where the remote file was blocked.
That is a vendor-concentration and shared-tenancy problem, not only a patching problem. The experimentation control plane sat in front of many customers' public sites. A signup-flow flaw, stolen credentials, a broadly scoped API token or a weak integration would all have the same shape: one write into a shared service, many production pages changed at once. Decoupling your CMS, tightening SSO or rotating secrets after the fact does not undo a day in which visitors already ran that script.
Decoupled and Git-based CMS architectures can shrink some of these risks for first-party content, and they are worth examining on their own terms. CrafterCMS documents a design in which authoring and delivery are separate systems with no shared database, content is stored as files in Git, and a deployer publishes outward from authoring to delivery. In addition, Crafter Cloud operates as a private SaaS option, and self-hosted deployments are supported. None of that makes a site immune to this kind of attack. If a delivery page still loads a compromised third-party script, that site (and only that site) can be affected even when the CMS itself was never breached. Git history helps you roll back first-party changes you control. It does not police a vendor snippet you do not.
What Enterprise Architects Should Do Next
If your sites use Optimizely Web Experimentation, treat this as an incident in your own environment, not only as a vendor outage.
First, inspect every project's Project JavaScript and every experiment's custom code, as Report URI advises, and look for code your team did not write. A snippet that is clean today may still have served the payload on November 16. Ask Optimizely which of your project IDs were changed, when, and how.
Second, review who and what can write to the account. Rotate user credentials, API tokens and integration secrets. Confirm how SSO and your identity provider are applied to the Optimizely tenant, and whether any service account is more powerful than it needs to be. Optimizely says it ended sessions and reset access for affected accounts. That does not replace your own review.
Third, treat third-party scripts as production code. Inventory every tag on public pages, especially checkout and account flows. Keep payment card collection in the payment provider's own cross-origin fields. If your pages collected card numbers directly on November 16, treat those cards as possibly exposed and follow your payment processor's process. Rotate session tokens or other secrets that were stored in cookies without the HttpOnly flag.
Fourth, put a Content Security Policy in front of those pages, with tight script-src and connect-src rules and reporting turned on. Allowing a vendor's CDN is not the same as knowing what that file will contain tomorrow. Avoid 'unsafe-eval' where you can.
Fifth, tighten the architecture conversation, not only the ticket. Decide which personalization, experimentation, analytics and tag-management services are allowed to run on production pages, what their blast radius is if the control plane is wrong, and how you would detect a change in a trusted script. A decoupled CMS and a Git-based publishing path can contain some classes of first-party compromise and make rollback auditable. They do not replace supply-chain due diligence for the JavaScript you load at runtime.
Visitors who used an affected site on November 16 should compare any cryptocurrency payment made that day with the address they intended to pay, watch card statements if they entered card details in a site's own form, and keep iPhones and iPads on a current iOS or iPadOS release. Those are the researchers' recommendations, not a finding that any one visitor was harmed.
The protocol of this incident is already familiar: a trusted vendor, a shared delivery path, and a write that customers could not see until the script was already running in their visitors' browsers. The architectural question is how much of that path an enterprise is prepared to keep surrendering.